Looking for the latest information on Adding Custom Http Headers? We've gathered comprehensive data, records, and insights about Adding Custom Http Headers.
Important Facts
Explore the key sources for Adding Custom Http Headers.
Latest News
Stay updated on Adding Custom Http Headers's newest achievements.
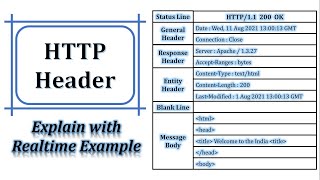
HTTP Headers | Realtime example of HTTP Header | HTTP Response header | HTTP Request Header
Modify Header by SelectorsHub | Test HTTP Headers Without Coding | Safe Alternative to ModHeader
Supercharge Your REST API with These Essential HTTP Headers
HTTP Headers and Cookies
Add Custom Headers via HTTP module in IIS 7/8/10 (For .net 1.1 legacy app)
How to Modify HTTP Headers Using Requestly
How to Modify HTTP Headers (Safe ModHeader Alternative) - Modify Header
Modify Header Value - Browser Extension Review
MORE Essential HTTP Headers
How to add a custom response header via IIS URL Re-write (Referrer-Policy)
Bypass ANY Website Restrictions (Modifying HTTP Headers) | picoCTF: Who Are You
Expert Insights
Data is compiled from public records and verified media reports.
Last Updated: October 27, 2026
Future Outlook
For 2026, Adding Custom Http Headers remains one of the most talked-about information profiles. Check back for the latest updates.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
In this video you will learn how to manipulate and modify any Part of the Adversary E/Simulation System. In this video on WMB Tutorials we will see how to Retrieving my blog: chiragbhalodia.com/2022/01/http-transaction-connection.html Topics: 00:00 Introduction 00:43 How to Install 01:35 What are This video is part of the Passport JS User Authentication Series. To view the entire series as a playlist, the link below: ... This tutorial will teach you how to modify/ In this video, we look deeper into critical security-related If you are still using .net 1.1 and set-up in a classic mode application pool. You are not able to change the PicoCTF web exploitation challenge by bypassing multiple client-side restrictions using