Ra - TryHackMe | Full Walkthrough (Including Spark Installation Fix)
REvil Corp: The Incident Responder's Guide to Mandiant Analysis & File Analysis with Redline!
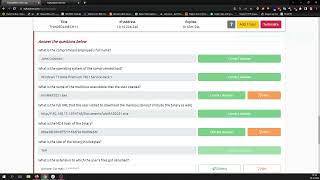
|-~S3R43o3~-| live @TryHackMe: REvil Corp - Investigate ransomware
TryHackMe #561 REvil Corp
REvil Ransomware Forensics with Redline Tool | Sadinokibi | TryHackMe
Full Guide
Data is compiled from public records and verified media reports.
Last Updated: October 26, 2026
Future Outlook
For 2026, Tryhackme Revil Corp remains one of the most searched-for information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
In this video, we are going through the In this video walk-through, we used Fireeye Redline to investigate a machine compromised with Sodinokibi Ransomware. Hi guys, in this video i am doing a room on In this video, we'll unpack the REvil Corp room from TryHackMe and delve into a Digital Forensics & Incident Response (DFIR ... ACCESS GRANTED Full walkthrough of the Ra room (WindCorp) on "Unmasking REvil Corp: The Incident Responder's Guide to Mandiant Analysis & File Analysis with Redline!" 🌟 Dive deep into ... Ransomware aka verschlüsselung gespeicherter Daten kann eine fiese Sache sein. Hier ein Ansatz zum lösen. Du möchtest ...