Looking for the latest information on A01 Broken Access Control Practice? We've compiled comprehensive data, records, and insights about A01 Broken Access Control Practice.
Main Features
Explore the main sources for A01 Broken Access Control Practice.
Developments
Stay updated on A01 Broken Access Control Practice's latest milestones.
OWASP Top 10 A01 – Broken Access Control (Theory) | Complete Explanation
A01:2025 Broken Access Control
Broken Access Control Explained 🔥 OWASP A01 | PortSwigger Practical
Cracking Broken Access Control (BAC) in Bug Bounty
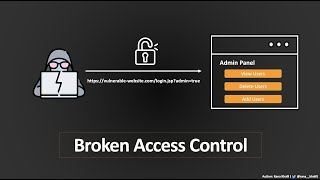
Broken Access Control | Complete Guide
Hackers Skip the Login: Broken Access Control | A01:2025
Broken Access Control Explained | OWASP A01:2021
Broken Access Control via Email Manipulation | IDOR Bug Bounty PoC | Bug Bounty POC
🔐 A01: Broken Access Control | 🧾 Summary
Broken Access Control POC using Burpsuite & OWASP Juice shop, a Burpsuite Tutorial #shorts #trending
How I Made $30,000 Hacking Broken Access Control
Detailed Analysis
Data is compiled from public records and verified media reports.
Last Updated: October 26, 2026
Summary
For 2026, A01 Broken Access Control Practice remains one of the most searched-for information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
Welcome to the OWASP Top 10 Series by ThunderCipher! In this video, we cover OWASP Top 10 Maintaining its position at in the Top Ten, 100% of the applications were tested for some form of Learn more about hacking & bug bounty In this video, I demonstrate a potential ... and challenges: app.hackinghub.io I've made over $30000 from one bug class: